The problem
A security platform needs more than working endpoints: it must establish trust, restrict access and make operational decisions auditable. TERVYQ is an ongoing project exploring these concerns through a practical backend and deployment environment.
Architecture
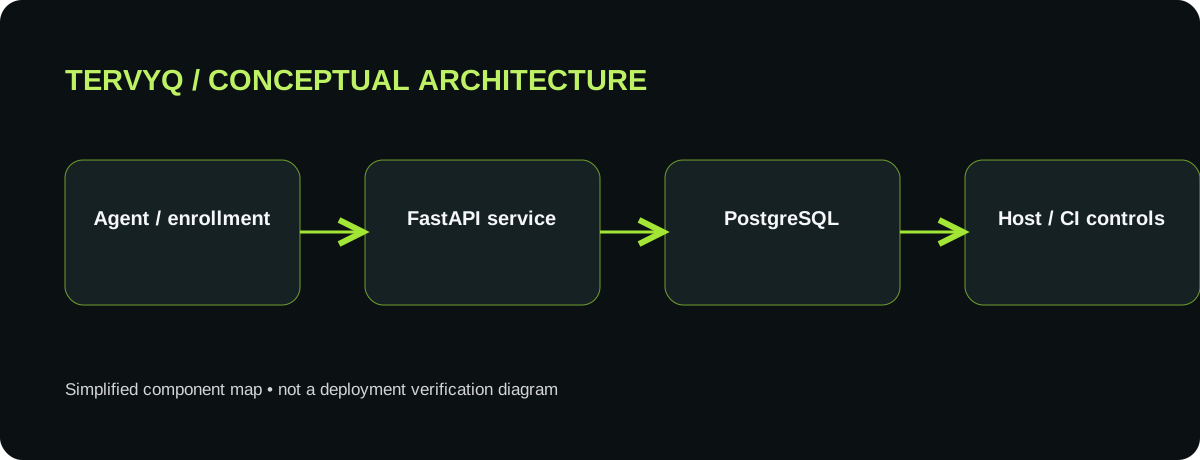
The diagram is a conceptual overview, not a claim that every planned subsystem is already deployed. The project uses a Python backend, PostgreSQL and Docker, with security controls at the host and application boundaries.
Engineering decisions
- Enrollment: agent enrollment tokens are modeled explicitly, with database privileges checked as part of development.
- Database boundaries: separate application and migration responsibilities help reduce routine access.
- Deployment: hardened Docker configuration, host firewall policy and SSH key authentication form part of the documented environment.
- Verification: tests, migration checks and CI/security scanning provide reviewable evidence rather than relying on implementation claims.
Current status and limits
TERVYQ remains in development. Its educational Google Cloud VM has restricted firewall/tag administration permissions, so host-level controls and cloud-level controls must not be conflated. A polished public demonstration and complete end-to-end operational evidence are still future work.
Evidence
Verified screenshot not yet published. This section will be updated when the original evidence is available.
Next steps
Expand end-to-end agent workflows, publish verified test and deployment evidence, and document the final operational boundaries.